One Login, No Separate Password
Your team signs in to Files.com with the same Google login they already use for Gmail and Workspace. There's no second password to hand out for file transfer, on the website or in the Desktop App.
Connect Files.com to Google. Now your Workspace users sign in to file transfer with the Google login they already have, no second password. On top of that login, Files.com sets who can reach which folders and keeps a record of everything that happens.
No credit card required · 7-day free trial · Live in minutes


Real companies. Real file flows. Real results.








Google already signs your people in everywhere else they work. Files.com uses that same Google login for file transfer: partner exchange, sending files to people outside the company, and taking large files in. And Files.com adds the folder controls Drive doesn't have.
Your team signs in to Files.com with the same Google login they already use for Gmail and Workspace. There's no second password to hand out for file transfer, on the website or in the Desktop App.
Give someone access in Google Workspace. Files.com makes their account the first time they sign in, with no setup step in between. (This is called JIT.) They're ready the moment they log in.
Because the account isn’t created until someone’s first login, you never pay for a person who has Google access but never logs in to Files.com. You pay for people who actually use it.
Set who can reach which folders. Keep a record of every file action. Put expiration dates on share links, and take large files from people outside your company. So when a partner or regulated handoff lands on you and Drive can't carry it, you don't reach for a second tool, and the audit has the record it needs.
Google’s MFA covers the people who sign in through Google. For partners and outside accounts Google doesn’t manage, Files.com adds its own 2FA, including hardware keys and authenticator apps. And it holds over SFTP, FTP, and WebDAV too, so a stolen partner password isn’t enough to reach your files, even on the protocol connections.
Google confirms who is signing in. It was never meant to decide which folders that person can touch, or to record what they do. Files.com adds that part, and it's the part an audit asks about.
Nine levels of access, per person or group, folder by folder. You can block a folder and fence off admins. Each person who signs in with Google reaches exactly the folders you granted, and nothing else.
Every sign-in, file action, and permission change is logged and exportable. You get an audit-grade record of document handoffs and share-link activity that Google Drive doesn’t keep for partner or regulated exchange.
The Google sign-in uses OAuth/OIDC, so accounts are made on first login rather than synced ahead of time (this is called JIT). To remove someone, turn off their access in the Google admin console and deactivate them in Files.com. You can do that by inactivity rule, by expiration date, or by hand, so an account doesn't sit active after the person is gone.
Allow or deny SFTP, FTP, and WebDAV per user or per group. A person who only needs the website never holds an open protocol door, and a machine account never gets a browser login.
The connection runs on Google's own OAuth 2.0 / OpenID Connect login. It's the same one Google already trusts for Gmail and Workspace. There's no special connector to build or keep running.
Keep at least one site administrator on a Files.com password instead of Google. If Google or your SSO setup ever has an outage, you can still get in and fix it instead of being locked out of your own site.
A Google login covers both the website and the Files.com Desktop App. SFTP, FTPS, FTP, and WebDAV connections keep their own keys or passwords, so partner and machine access stays separate from the people signing in with Google.
Files.com respects the MFA a Workspace admin already requires for the people who sign in through Google. For the partners and outside accounts Google never sees, Files.com adds its own 2FA: hardware keys and authenticator apps. So every account that touches your files is behind a second factor, not just the ones inside Workspace.
Pick Google from the sign-in providers in Files.com and save. There's barely anything to set up. For people who already have Files.com accounts, set their login method to Google, matching their Google email. From then on they click Log in with Google.
Nothing extra to set up. Accounts are made on first Google login. Since first-login creation can't remove people, deactivate departed users in Files.com as well.
A Workspace user clicks Sign in with Google on the Files.com login page. They land in their account with the Google login they use everywhere else.
A newly approved Google user signs in for the first time. Files.com makes their account on the spot, already set to the folders and permissions their group carries.
A team on Google Drive uses a Files.com inbox to collect large files from an outside partner who has no Google account. Every handoff is logged. That’s the gap Drive leaves.
A partner account that doesn't sign in through Google can be required to use Files.com 2FA, and the requirement holds over their SFTP connection.

Put a GCS bucket behind the same Google login. File access and storage live under one sign-in.
Learn More
Connect Drive as storage and put folder permissions and an audit trail on top of the same Google login.
Learn MoreGive an outside partner a branded upload link. They send you files with no Files.com account and no Workspace seat, and every upload lands in the folder you chose.
Learn MoreGroup-based permissions sit on top of the Google login, and you can make someone a folder admin without handing them the whole site.
Learn MoreApril 13–15, 2027 · Las Vegas, NV
Files.com builds deeply on Google Cloud Storage, Drive, and Workspace, so of course we’ll be on the floor at Google Cloud Next telling our File Orchestration story. The legacy MFT vendors won’t be there.
See Files.com At Google Cloud Next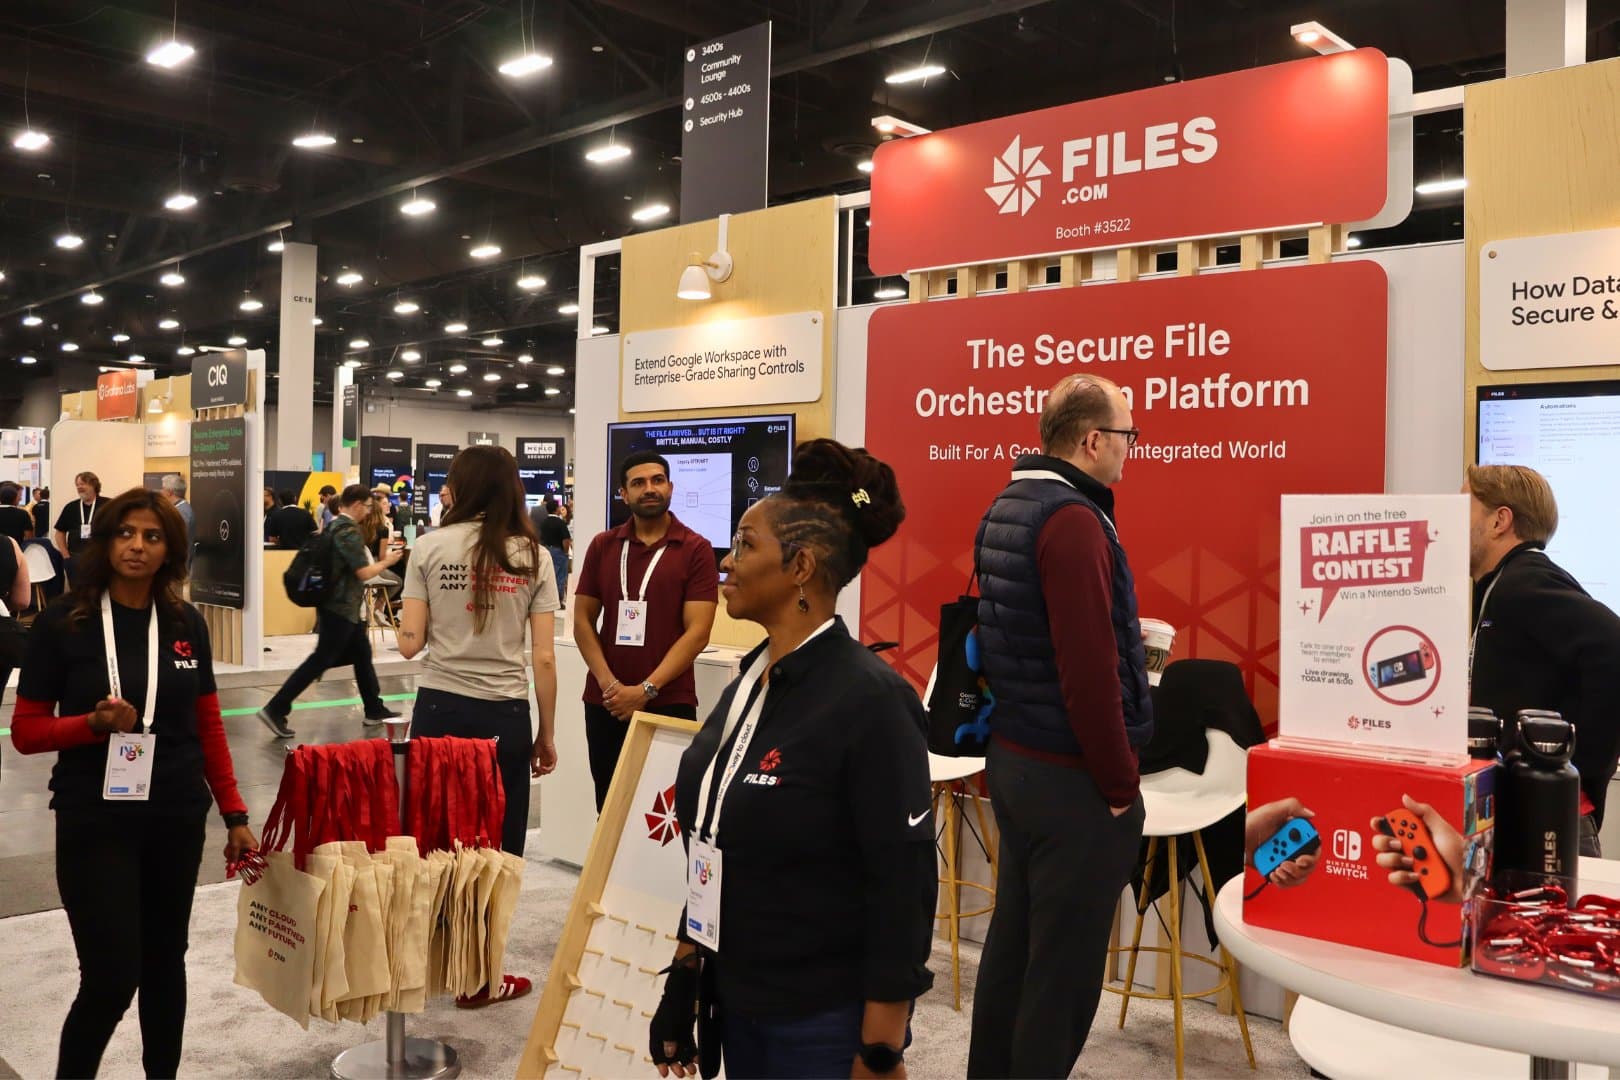
The shared service had to support temporary access, persistent system exchanges, automated delivery, and the fixed-network requirements of outside partners.
Read The Story

Each payer or provider now has an isolated path from its own SFTP credential and folder to a dedicated cloud storage bucket.
Read The Story
A root-level cross-workspace sync and delta pass moved 585 GB from a live tenant, establishing a pattern for closing other acquisition-era workspaces.
Read The Story

Google Workspace stayed in place for internal collaboration while Files.com became the governed, scalable route for every external exchange.
Read The Story
“Files.com's strengths are simplicity, ease of use, and the cloud connectors. We don't have to invent custom infrastructure for every partner.”

“Files.com is versatile — it can manage many different situations from a single platform. We've consolidated multiple tools onto it.”

“Files.com is robust and scales to a large enterprise. We get multiple files per minute, per second — and we're a 24/7 organization, so everything has to always be up.”

What the Google login covers on Files.com, what happens when someone leaves Workspace, and whether you pay for people who never sign in.
Yes. Files.com uses Google's own OAuth 2.0 / OpenID Connect login, so your team signs in to Files.com with the same Google login they use for Gmail and Google Workspace.
No. SCIM provisioning on Files.com works only over SAML connections, and the Google sign-in uses OAuth/OIDC instead. With Google, Files.com makes accounts on first login (JIT) but can't turn people off automatically. If you need that, connect over SAML instead.
Deprovisioning a Google SSO user takes two steps: turn off their access in the Google Workspace admin console, then deactivate their Files.com account. Removal isn't automatic with Google, because Files.com makes accounts on first login (JIT) rather than syncing them. You can deactivate by an inactivity rule, an expiration date, or by hand.
No. You pay for people who actually use Files.com. Since an account isn't created until someone's first login, you never pay for a person who has Google access but never logs in. See how Files.com pricing counts seats.
No. Signing in with Google works for the website and the Files.com Desktop App. SFTP, FTP, and WebDAV connections use an SFTP key, an API key, or a password instead.
Files.com lets you set who can reach which folders, keeps a record of every file action, puts expiration dates and controls on share links, and takes large files from people outside your company who have no Google account. That's the control Google Drive doesn't give you for partner or regulated file exchange.
Files.com matches on email address. For an existing user, set their Files.com username and email address to the email of the Google account they sign in with. A new user doesn't need matching: Files.com creates the account from the Google identity on first login.
A suspended Workspace account can no longer sign in to Files.com. Files.com authenticates against Google on every login, so the suspension takes effect immediately. The Files.com account itself remains until you deactivate it, by inactivity rule, expiration date, or by hand.
Yes. Your team signs in with Google while outside partners use Files.com credentials scoped to their own folders. One platform serves both, under one audit trail.
Start a 7-day free trial. Set Google as your sign-in provider, log in with an existing Workspace account, and see it work on your own files.
No credit card required • 7-day free trial • Live in minutes